Flash CTF - Registry 101
Registry 101 Writeup
Overview
Registry 101 is a Windows registry forensics challenge. Players are handed a copy of a user's registry hive and must prove that a specific set of documents was opened on the machine, even though the suspect denies it. The evidence isn't sitting in the hive itself. It only shows up once you bring the hive's transaction logs into the picture.
Reconnaissance
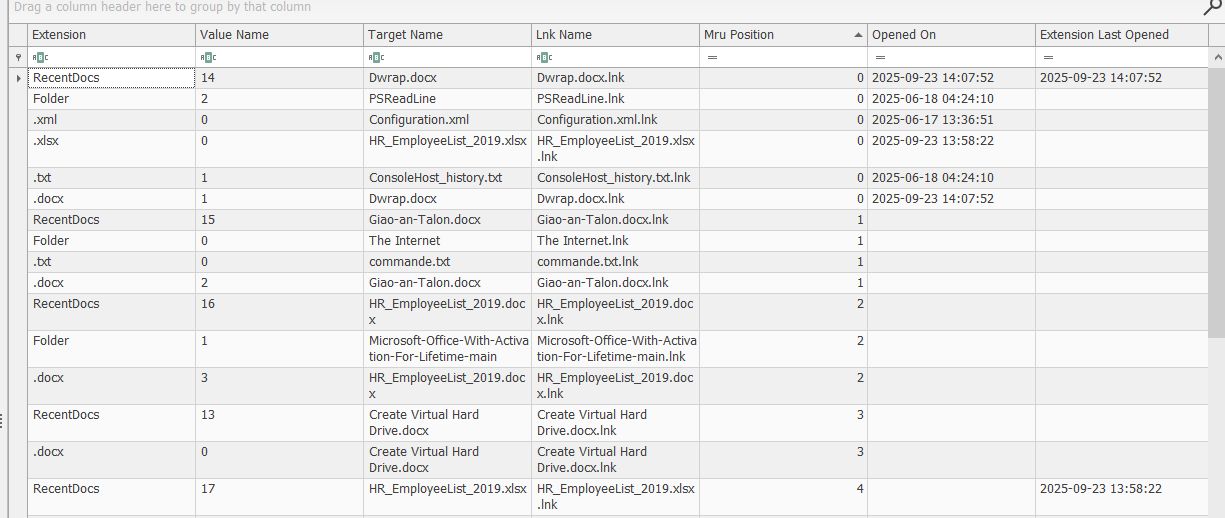
The provided evidence is a copy of the user's ntuser.dat hive plus its two associated transaction logs. Loading just ntuser.dat into Registry Explorer and navigating to RecentDocs shows recent activity, but nothing that resembles a flag. The entries that matter simply aren't there yet:
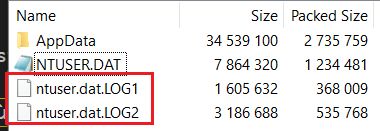
The two log files sitting alongside the hive are the giveaway that some in-flight registry writes haven't been merged into the main file:
Exploitation
Registry Explorer can replay a hive's transaction logs against it at load time instead of reading the hive on its own. Pointing it at ntuser.dat and supplying both .LOG files reconstructs the fully up-to-date state of the hive, including the writes that were still pending:
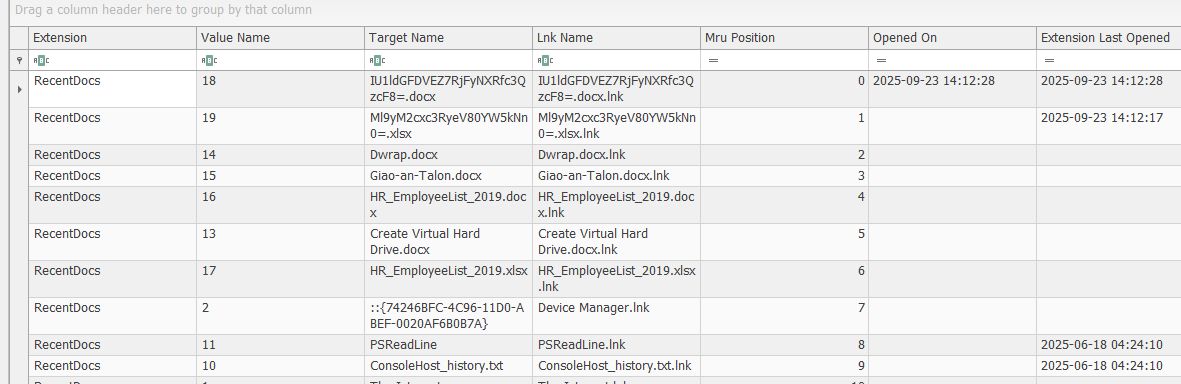
With the logs replayed, RecentDocs reveals two recently opened files whose names are not ordinary filenames at all:
IU1ldGFDVEZ7RjFyNXRfc3QzcF8=.docx
Ml9yM2cxc3RyeV80YW5kNn0=.xlsx
The base part of each filename is Base64. Decoding both and concatenating them in order reconstructs the flag:
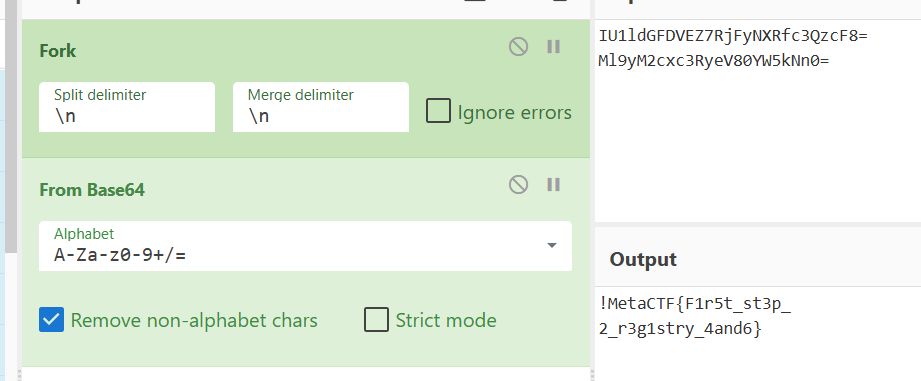
Getting the Flag
echo -n "IU1ldGFDVEZ7RjFyNXRfc3QzcF8=" | base64 -d
echo -n "Ml9yM2cxc3RyeV80YW5kNn0=" | base64 -d
Concatenating the two decoded fragments gives the flag exactly as the author encoded it into the evidence, with the leading ! as part of it:
!MetaCTF{F1r5t_st3p_2_r3g1stry_4and6}